October 29, 2026
October 29, 2026
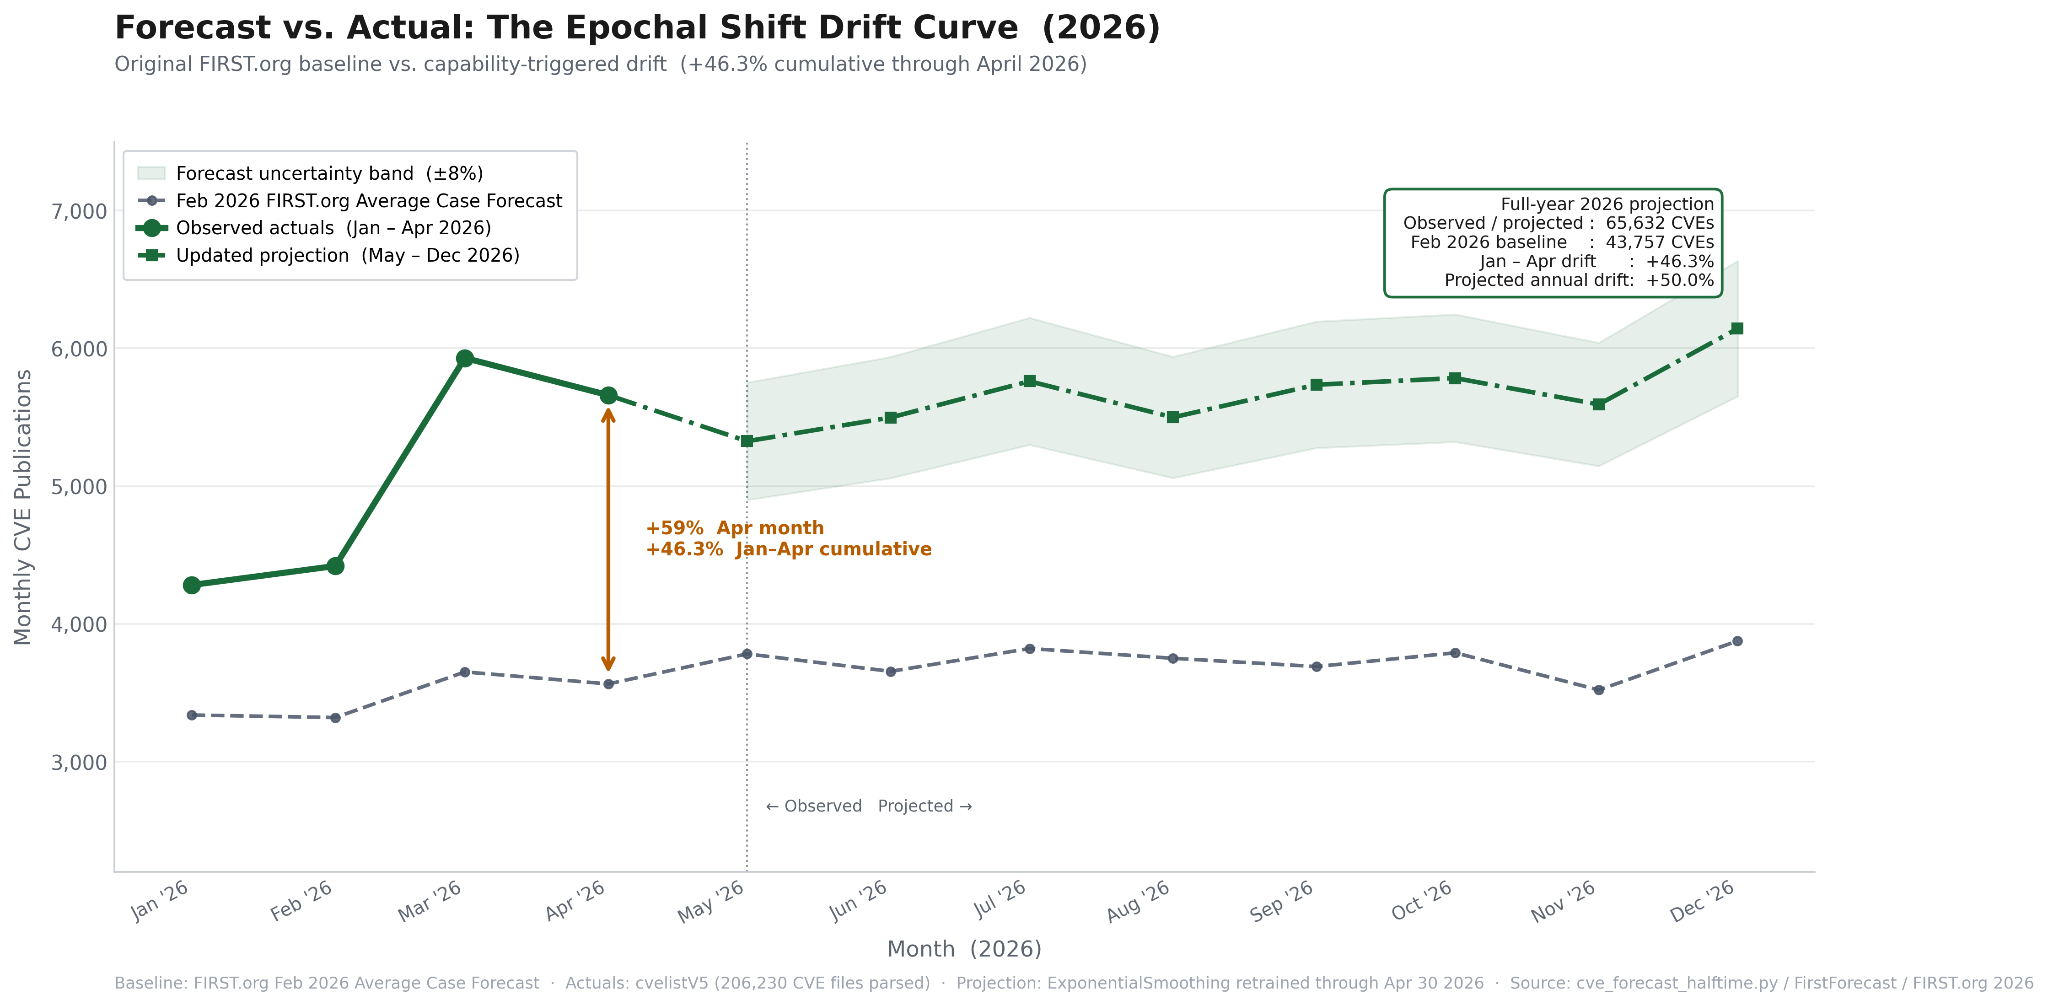
Microsoft’s July 2026 Patch Tuesday addressed at least 570 vulnerabilities across Windows and other products, nearly three times the company’s previous monthly record. Almost 60 flaws were rated critical, and three were classified as zero-days, including two already exploited in real attacks. Among the most urgent issues were privilege-escalation vulnerabilities in Active Directory Federation Services and SharePoint, while a publicly disclosed BitLocker bypass could expose encrypted data when an attacker has physical access to a device. Microsoft also fixed a critical Copilot vulnerability that could allow a malicious website opened in Edge for Android to send crafted prompts and execute code remotely.
Microsoft attributed the unusually large release to AI-assisted vulnerability discovery, which is finding security defects more quickly across extensive codebases. However, AI is also helping attackers develop working exploits faster, raising concerns that Microsoft’s traditional exploitability ratings may underestimate how rapidly vulnerabilities can be weaponized. The broader software industry is similarly increasing its patch frequency, with Adobe, Google and others releasing more updates. Because of the exceptional volume of fixes and the possibility of stability problems, organizations should prioritize actively exploited and critical flaws, test updates carefully and maintain reliable backups before widespread deployment.
Source: KrebsOnSecurity